Navigating international privacy regulations is critical for global organizations. This Cross-Border Biometric Data Transfer Compliance Advisory Letter provides essential legal guidance on securely managing sensitive physiological data across jurisdictions while adhering to strict frameworks like GDPR and CCPA. Ensure your business minimizes legal risks and maintains data integrity during international transfers. To assist your implementation, below are some ready to use template.
Image cover: Compliance Advisory: Best Practices and Templates for Cross-Border Biometric Data Transfers
Letter Samples List
- Initial Cross-Border Biometric Data Transfer Compliance Advisory Letter
- Client Engagement Letter for Biometric Data Privacy Counsel
- Multinational Employee Biometric Data Consent Advisory Letter
- Vendor Biometric Information Processing Agreement Advisory Letter
- International Facial Recognition Data Transfer Compliance Letter
- Biometric Data Protection Impact Assessment Executive Letter
- Global Fingerprint Data Storage and Transfer Advisory Letter
- Jurisdictional Risk Assessment Letter for Biometric Data Exports
- Biometric Data Breach Notification and Remediation Advisory Letter
- Regulatory Agency Biometric Data Transfer Inquiry Response Letter
- Joint Controller Biometric Data Sharing Agreement Advisory Letter
- Overseas Data Center Biometric Security Compliance Advisory Letter
- Corporate Policy Update for Biometric Data Transfer Advisory Letter
Initial Cross-Border Biometric Data Transfer Compliance Advisory Letter
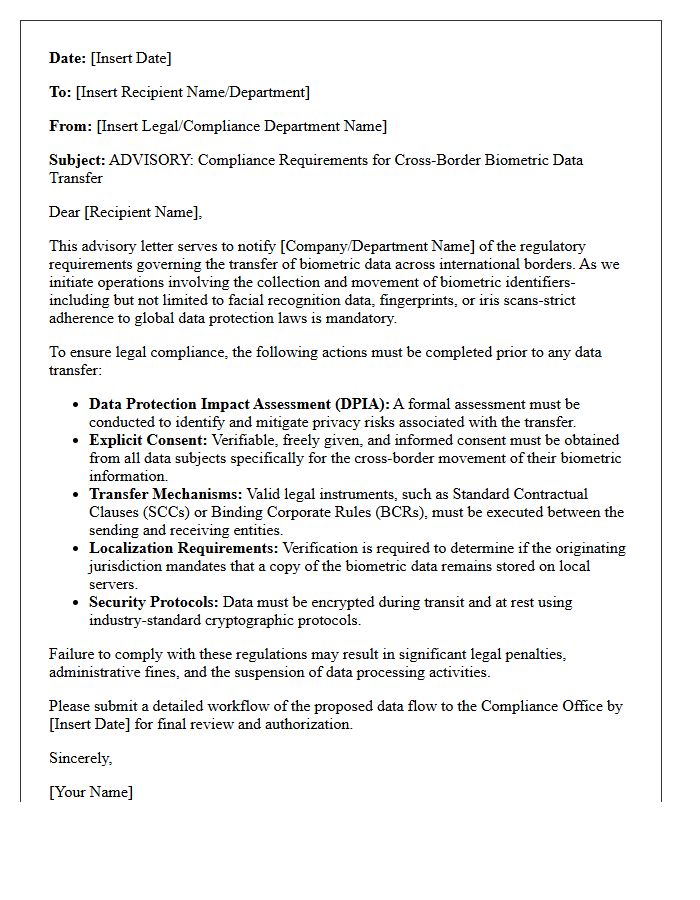
The Initial Cross-Border Biometric Data Transfer Compliance Advisory Letter serves as a formal notification regarding the legal requirements for moving sensitive identifiers across international boundaries. Organizations must ensure strict adherence to data protection regulations to avoid severe penalties. Key priorities include conducting impact assessments, obtaining explicit consent, and implementing robust encryption. This advisory acts as a critical roadmap for maintaining regulatory compliance while managing global information flows, ensuring that biometric privacy remains protected under evolving cybersecurity frameworks and international governance standards.
Client Engagement Letter for Biometric Data Privacy Counsel
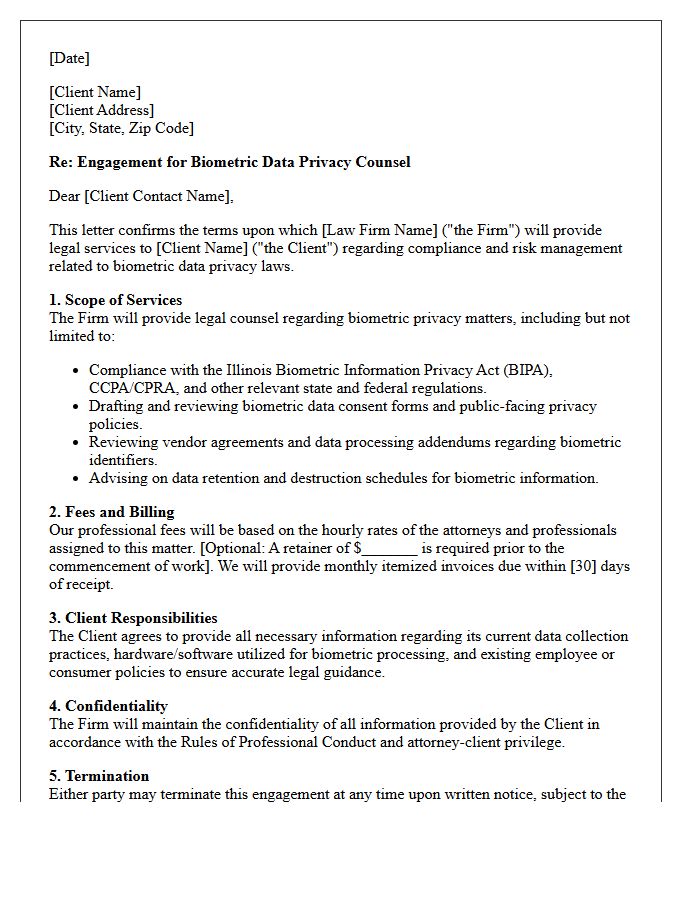
A Biometric Data Privacy Counsel engagement letter is a critical legal contract defining the scope of representation regarding sensitive identifiers like fingerprints or facial geometry. It must clearly outline compliance strategies for regulations like BIPA, risk assessment protocols, and fee structures. This document ensures attorney-client privilege while establishing protocols for data breach responses and litigation defense. For businesses, this agreement serves as the foundational protection against class-action lawsuits, ensuring that biometric collection, storage, and written consent processes align with evolving privacy statutes and industry standards.
Multinational Employee Biometric Data Consent Advisory Letter
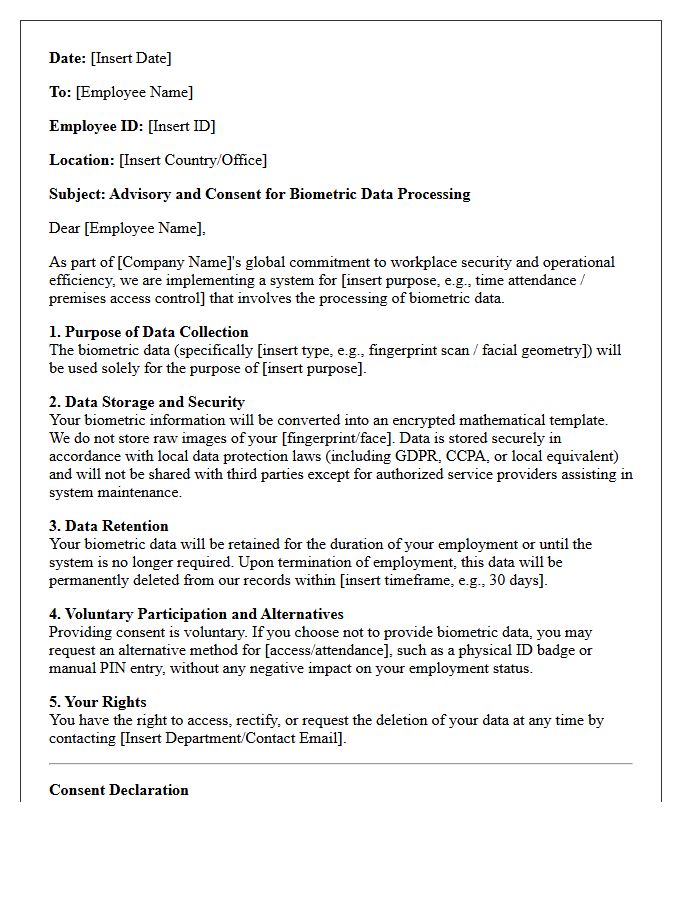
A Multinational Employee Biometric Data Consent Advisory Letter is a critical compliance document used to inform global staff about the collection of unique physical identifiers. It must clearly outline the legal basis for processing sensitive information under frameworks like GDPR or CCPA. Organizations must ensure transparency regarding data storage, security measures, and the specific purpose of biometric use. Providing a clear opt-out mechanism is essential to respect individual privacy rights. This letter mitigates legal risks by documenting informed consent and maintaining strict adherence to diverse international data protection regulations across different jurisdictions.
Vendor Biometric Information Processing Agreement Advisory Letter
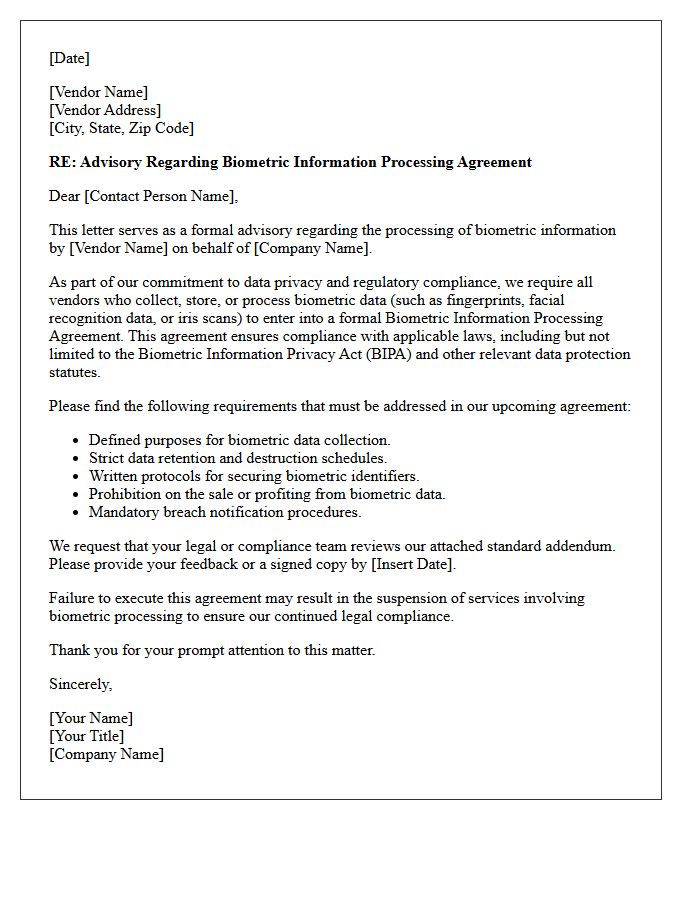
The Vendor Biometric Information Processing Agreement Advisory Letter is a critical legal notice ensuring third-party compliance with data privacy regulations like BIPA. It informs vendors of their specific obligations regarding the collection, storage, and deletion of sensitive biometric identifiers. This letter acts as a formal safeguard, requiring partners to implement robust security protocols and obtain necessary consent. By establishing these contractual mandates, organizations mitigate legal liability and protect consumer privacy, ensuring that all biometric processing aligns with evolving statutory requirements and data protection best practices.
International Facial Recognition Data Transfer Compliance Letter
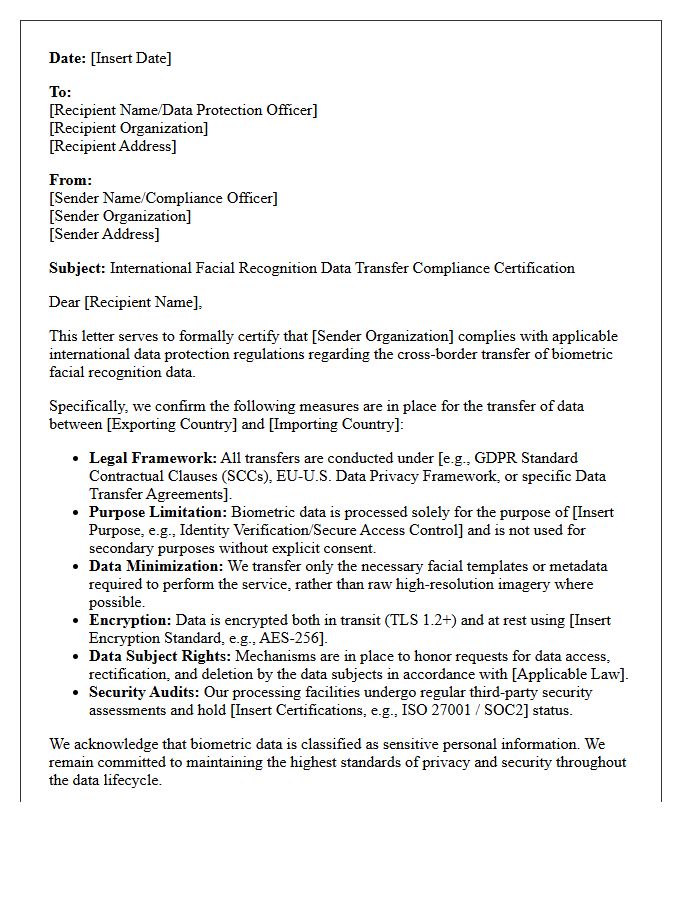
An International Facial Recognition Data Transfer Compliance Letter is a critical legal document used to authorize the cross-border movement of sensitive biometric information. It ensures that data sovereignty laws, such as GDPR or CCPA, are strictly followed when transferring facial templates between jurisdictions. This letter must detail the specific security protocols, the legal basis for processing, and the verified consent mechanisms in place. Maintaining this documentation is essential for organizations to mitigate legal risks and demonstrate accountability during international audits of facial recognition systems.
Biometric Data Protection Impact Assessment Executive Letter
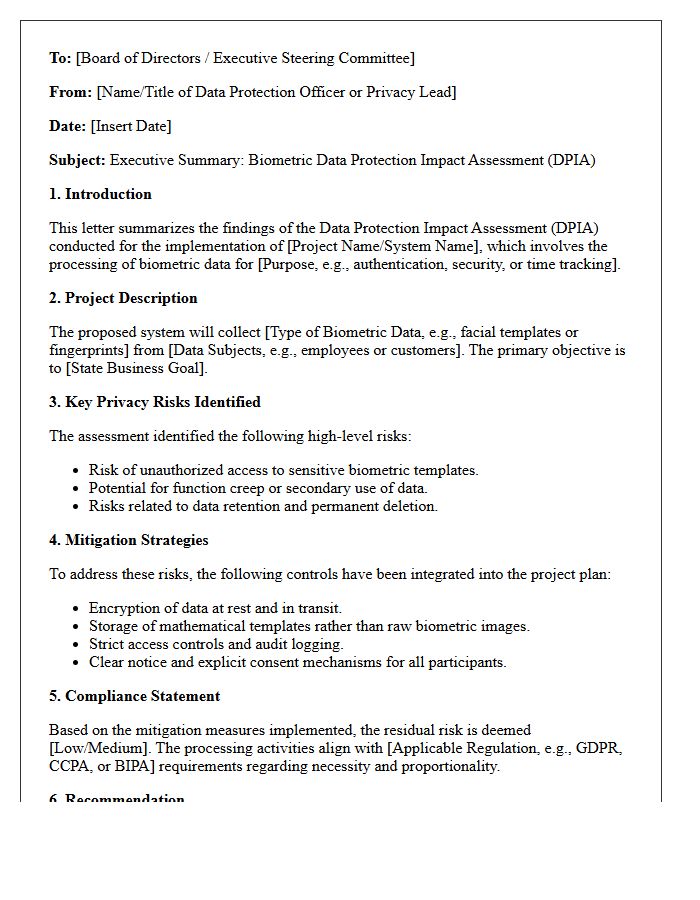
The Biometric Data Protection Impact Assessment (DPIA) Executive Letter is a high-level summary designed for leadership oversight. It highlights critical risks associated with processing sensitive biological identifiers, such as fingerprints or facial recognition data. This document confirms that the organization has evaluated regulatory compliance under frameworks like GDPR. It outlines necessary mitigation strategies to prevent unauthorized access and ensures that the deployment of biometric systems balances operational needs with individual privacy rights. Ultimately, it serves as formal accountability for ethical data governance and legal risk management.
Global Fingerprint Data Storage and Transfer Advisory Letter
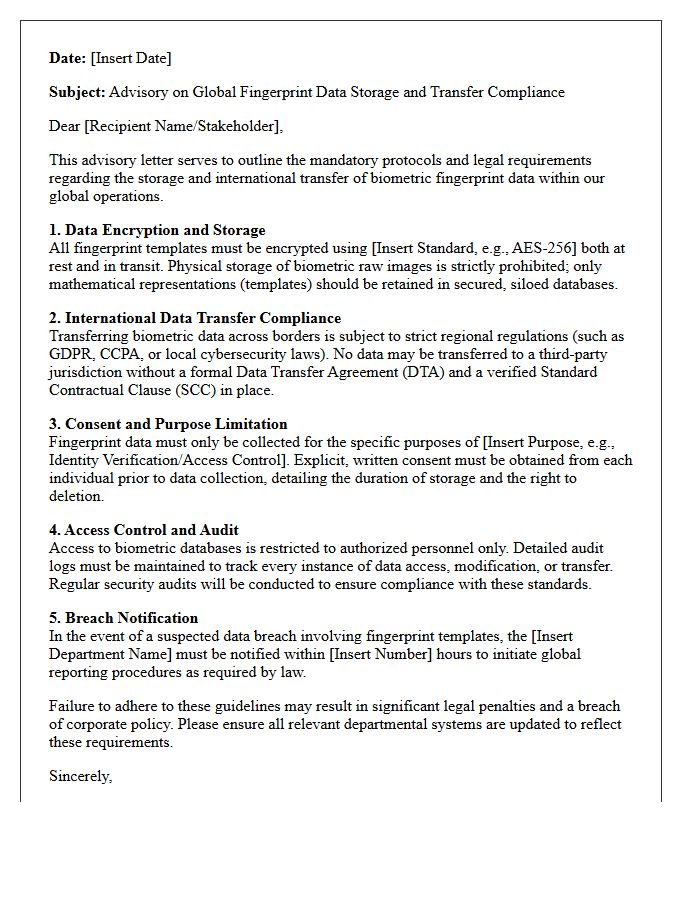
The Global Fingerprint Data Storage and Transfer Advisory Letter outlines critical compliance mandates for managing biometric identifiers. Organizations must prioritize data sovereignty and strict encryption protocols when moving sensitive templates across international borders. This advisory emphasizes that biometric privacy laws, such as GDPR and CCPA, require explicit user consent and robust audit trails. Failure to implement these security standards can lead to severe legal liabilities and data breaches. Ensuring interoperability while maintaining cryptographic protection is essential for any entity handling global fingerprint databases and cross-border digital identity verification processes.
Jurisdictional Risk Assessment Letter for Biometric Data Exports
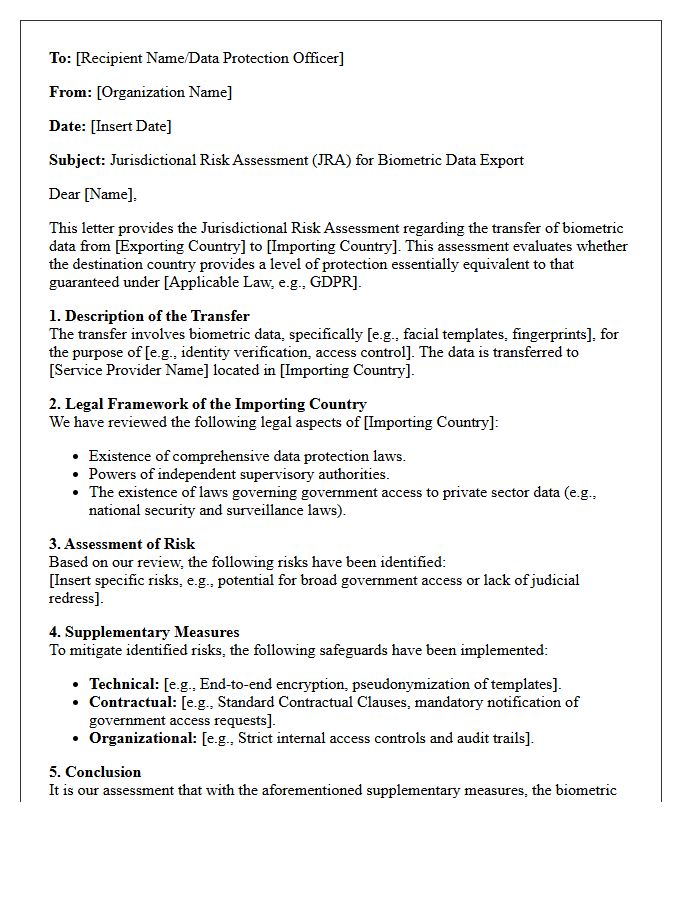
A Jurisdictional Risk Assessment Letter is a critical legal document evaluating the data protection standards of a destination country before transferring biometric information. Organizations must assess whether the recipient's legal framework provides equivalent protection to domestic privacy laws, such as GDPR. This assessment identifies potential surveillance risks, legal recourse for individuals, and the necessity of supplementary measures like encryption. Ensuring compliance through this letter mitigates the threat of regulatory fines and legal challenges, making it an essential component for the cross-border transfer of highly sensitive biometric data.
Biometric Data Breach Notification and Remediation Advisory Letter
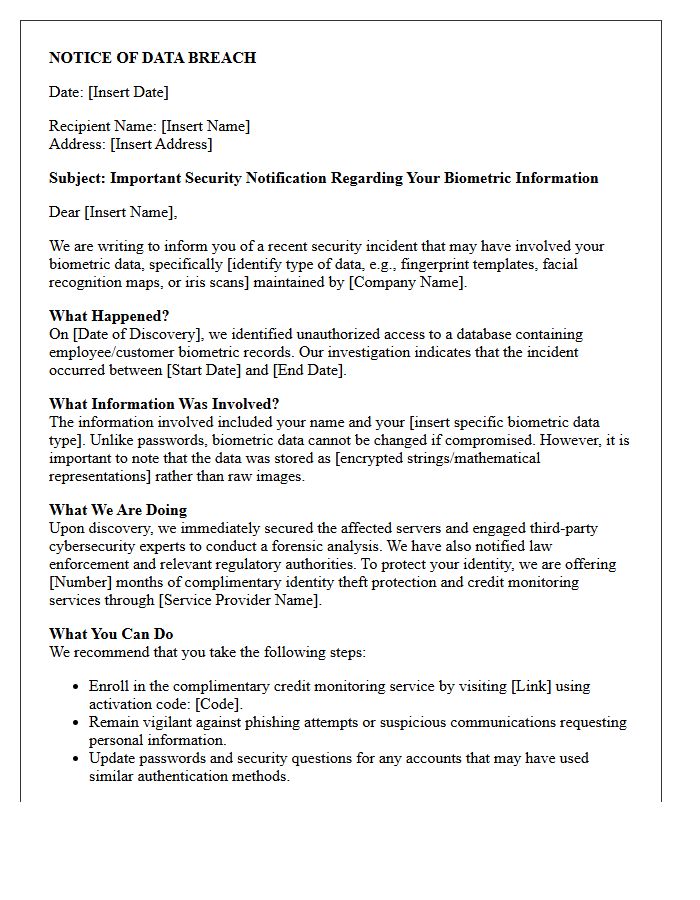
A Biometric Data Breach Notification and Remediation Advisory Letter is a formal communication sent to individuals after sensitive identifiers, such as fingerprints or facial recognition data, are compromised. Unlike passwords, biometric markers are permanent and cannot be changed, making immediate risk mitigation essential. The letter outlines the nature of the exposure, potential identity theft threats, and required remediation steps, such as freezing credit or monitoring accounts. Organizations must provide these notices to comply with legal mandates and ensure transparent incident response protocols to protect affected users.
Regulatory Agency Biometric Data Transfer Inquiry Response Letter
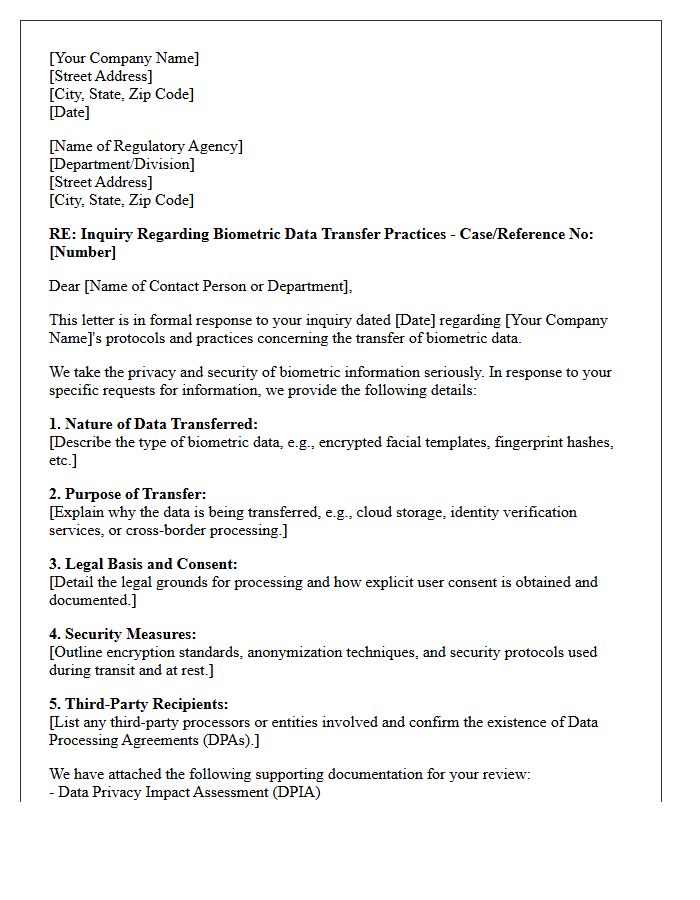
A Regulatory Agency Biometric Data Transfer Inquiry Response Letter is a formal document addressing government concerns regarding the movement of sensitive biometric identifiers across borders. It must justify legal compliance with data protection frameworks, such as GDPR or CCPA. Organizations must detail their encryption protocols, storage security, and the explicit consent mechanisms used for users. Providing a precise explanation of the necessity and proportionality of the transfer is essential to mitigate legal risks, avoid substantial regulatory fines, and ensure continued international operational authority.
Joint Controller Biometric Data Sharing Agreement Advisory Letter
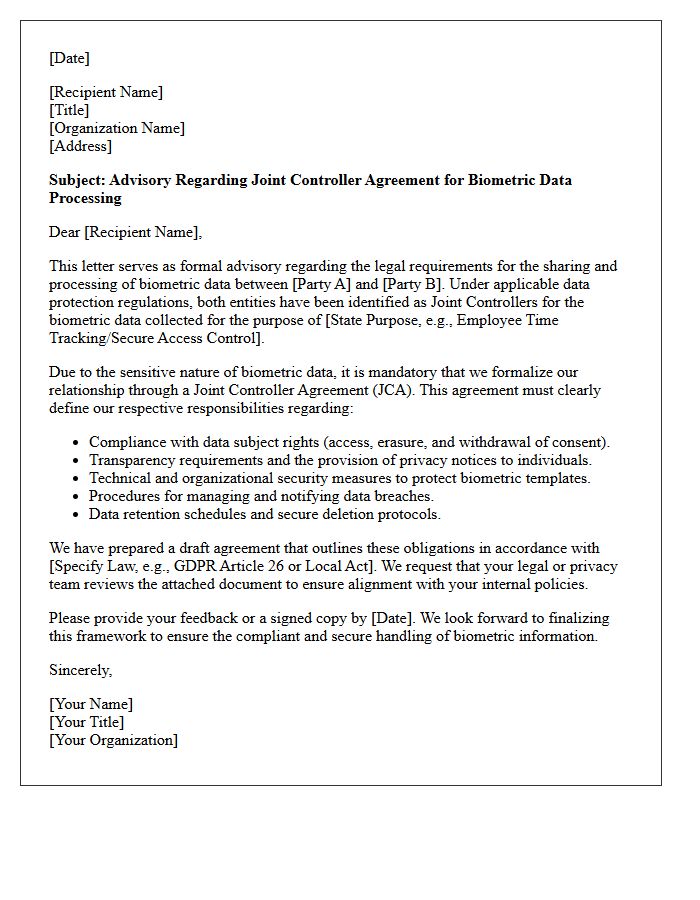
The Joint Controller Biometric Data Sharing Agreement Advisory Letter provides essential guidance for organizations processing sensitive physical identifiers. It emphasizes that when multiple parties determine the purposes of processing, they must establish a formal contract defining legal responsibilities under data protection laws. This document ensures compliance by outlining transparency requirements, security protocols, and individual rights. Businesses must verify that their agreements include specific liability clauses and governance frameworks to mitigate risks associated with biometric privacy breaches and regulatory scrutiny during cross-organizational data exchanges.
Overseas Data Center Biometric Security Compliance Advisory Letter
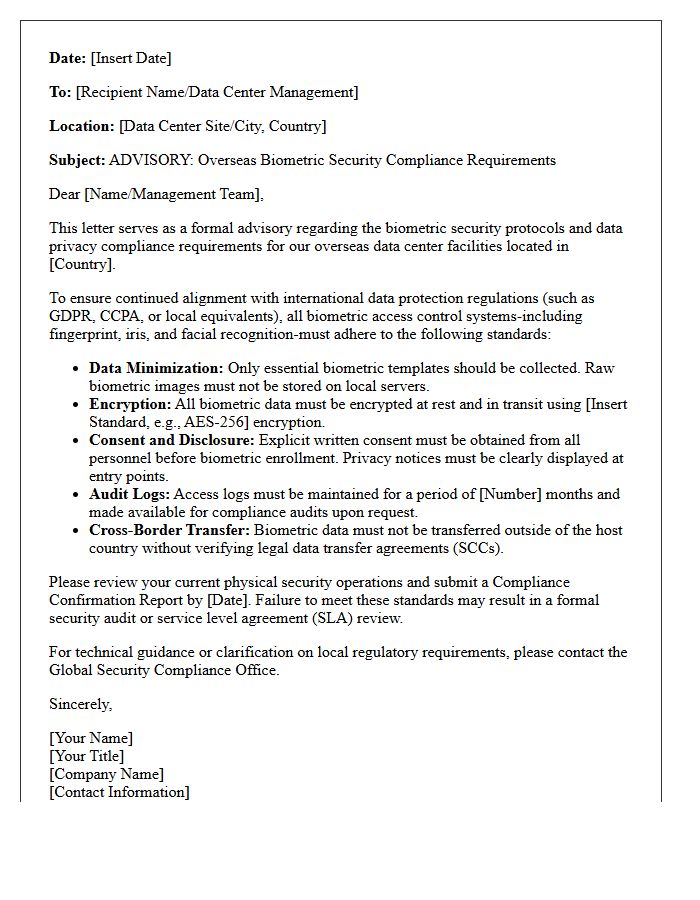
An Overseas Data Center Biometric Security Compliance Advisory Letter is a critical document ensuring facilities meet international regulatory standards for physical access control. It highlights the legal obligations regarding the collection, storage, and processing of sensitive biological markers. Organizations must prioritize these advisories to mitigate risks associated with data privacy breaches and cross-border jurisdictional conflicts. Understanding these requirements is essential for maintaining operational integrity and ensuring that biometric authentication protocols align with global governance frameworks like GDPR or local cybersecurity mandates.
Corporate Policy Update for Biometric Data Transfer Advisory Letter
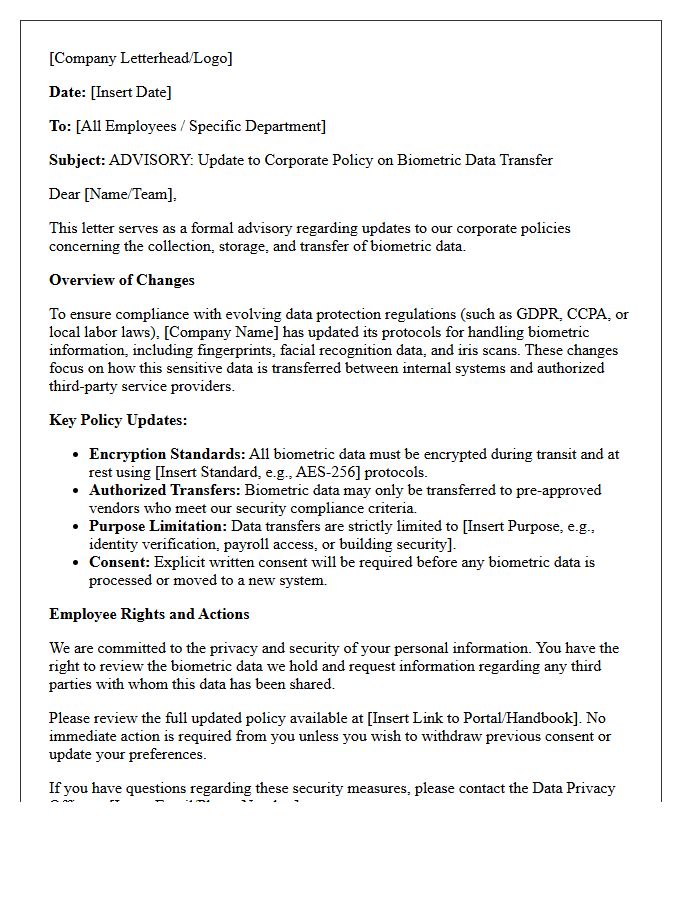
The Corporate Policy Update outlines mandatory protocols for the international transfer of employee and client information. This advisory letter emphasizes strict compliance with global privacy regulations like GDPR and CCPA. Organizations must implement end-to-end encryption and obtain explicit consent before moving biometric data across borders. Failure to adhere to these standardized security frameworks can lead to significant legal liabilities. All departments are required to review the updated data governance guidelines to ensure secure processing, storage, and cross-border transmission of sensitive identifiers within the corporate infrastructure.
What is a Cross-Border Biometric Data Transfer Compliance Advisory Letter?
This advisory letter is a formal legal notification or internal directive outlining the regulatory requirements and risk mitigation strategies for transferring sensitive biometric identifiers across international jurisdictions, ensuring alignment with laws like GDPR, CCPA, or PIPL.
What are the primary legal triggers for issuing this compliance advisory?
The letter is typically triggered when an organization intends to store, process, or transmit biometric templates-such as facial recognition data or fingerprints-outside of the country of origin, necessitating a Data Transfer Impact Assessment (DTIA) and adherence to local data sovereignty rules.
Which regulatory frameworks govern the cross-border movement of biometric data?
Compliance is primarily governed by regional data protection authorities, utilizing mechanisms such as Standard Contractual Clauses (SCCs), Binding Corporate Rules (BCRs), and specific biometric privacy statutes like Illinois' BIPA or China's Personal Information Protection Law.
What key elements must be included in the advisory letter to ensure enforceability?
The letter must include the explicit legal basis for transfer (such as informed consent), a detailed description of the security measures (encryption and anonymization), the identification of the data importer, and a clear outline of the data subject's rights in the recipient jurisdiction.
How does a compliance advisory letter mitigate corporate liability?
By documenting the due diligence process and establishing a formal protocol for international data flows, the advisory letter serves as evidence of "privacy by design," helping to shield the organization from administrative fines, litigation, and reputational damage resulting from unauthorized data exports.
Comments